Fail-Closed Secrets Scanning: Closing the Gaps in Historical Exposure for Insurance Broker Core
Today, the insurance-broker-core platform gains a new fail-closed gate on its full history: every commit, old and new, is now scanned for secrets before it can pass. This closes the last loophole for accidental credential exposure, making historical codebase hygiene enforceable by contract.
 Jadda Helpifyr2 min read
At a glance
72
merged changes
21
code projects involved
Most changes in
- helpifyr-fabric11
- insurance-broker-core11
- jhf-deployment7
Underlined terms are explained: just hover or tap.
Imagine an urgent audit after a third-party breach: every historical commit in your insurance platform is now under scrutiny for leaked secrets. Until today, even the most rigorous CI pipelines could only guarantee new code was clean, leaving years of legacy commits as a blind spot. With a single overlooked credential, the cost is not just technical debt, but regulatory risk and real-world exposure.
01Why it matters
Why This Day Mattered
Operators, compliance leads, and developers can now assert with evidence that no credential, API key, or secret has ever slipped into the repository at any point in its history. This makes external audits, regulatory reviews, and incident response both faster and more credible, as there is no longer a need for manual retroactive scans or hope-based trust in legacy hygiene. For developers, it means no more anxiety about inherited codebase risks and no more firefighting after-the-fact.
The closed UTC day 2026-08-14 resolved into 72 merged PRs across 21 repos, led by helpifyr-fabric (11), insurance-broker-core (11), jhf-deployment (7).
02What changed
What Actually Changed
A fail-closed CI gate now scans the entire repository history for secrets before any change is accepted. If any secret is detected, the change is blocked until the exposure is resolved and scrubbed. This applies retroactively, not just to new commits, making the check a contract on the full codebase lineage. The mechanism is enforced via CI and is tied directly to the SBOM and permission-matrix audits, ensuring that no historical commit escapes scrutiny.
03Why it holds better now
Why It Holds Better Now
The platform is now technically safer because accidental credential exposure is no longer a function of developer vigilance alone. The fail-closed gate makes it impossible for secrets to persist in the repository, even in old branches or rebased histories. This is a hard guarantee, not a best effort: the enforcement is machine-verifiable and blocks all paths to exposure, including edge cases like force-pushes or replays of old code.
04Food for thought
Want to Know More?
How might this historical secrets scanning gate be extended to enforce compliance for third-party dependencies and binary artifacts, preventing credential leaks from less-visible supply chain sources?
Terms in this post
- fail-closed
- Block when in doubt: if evidence is missing, the action does not run.
- PR
- Pull request: a reviewed code change that gets merged into the project.
- repo
- Repository: a code project under version control.
- operator
- The person or team running the system.
What would this look like in your company?
A pilot shows it with a real process.
More on Security
See all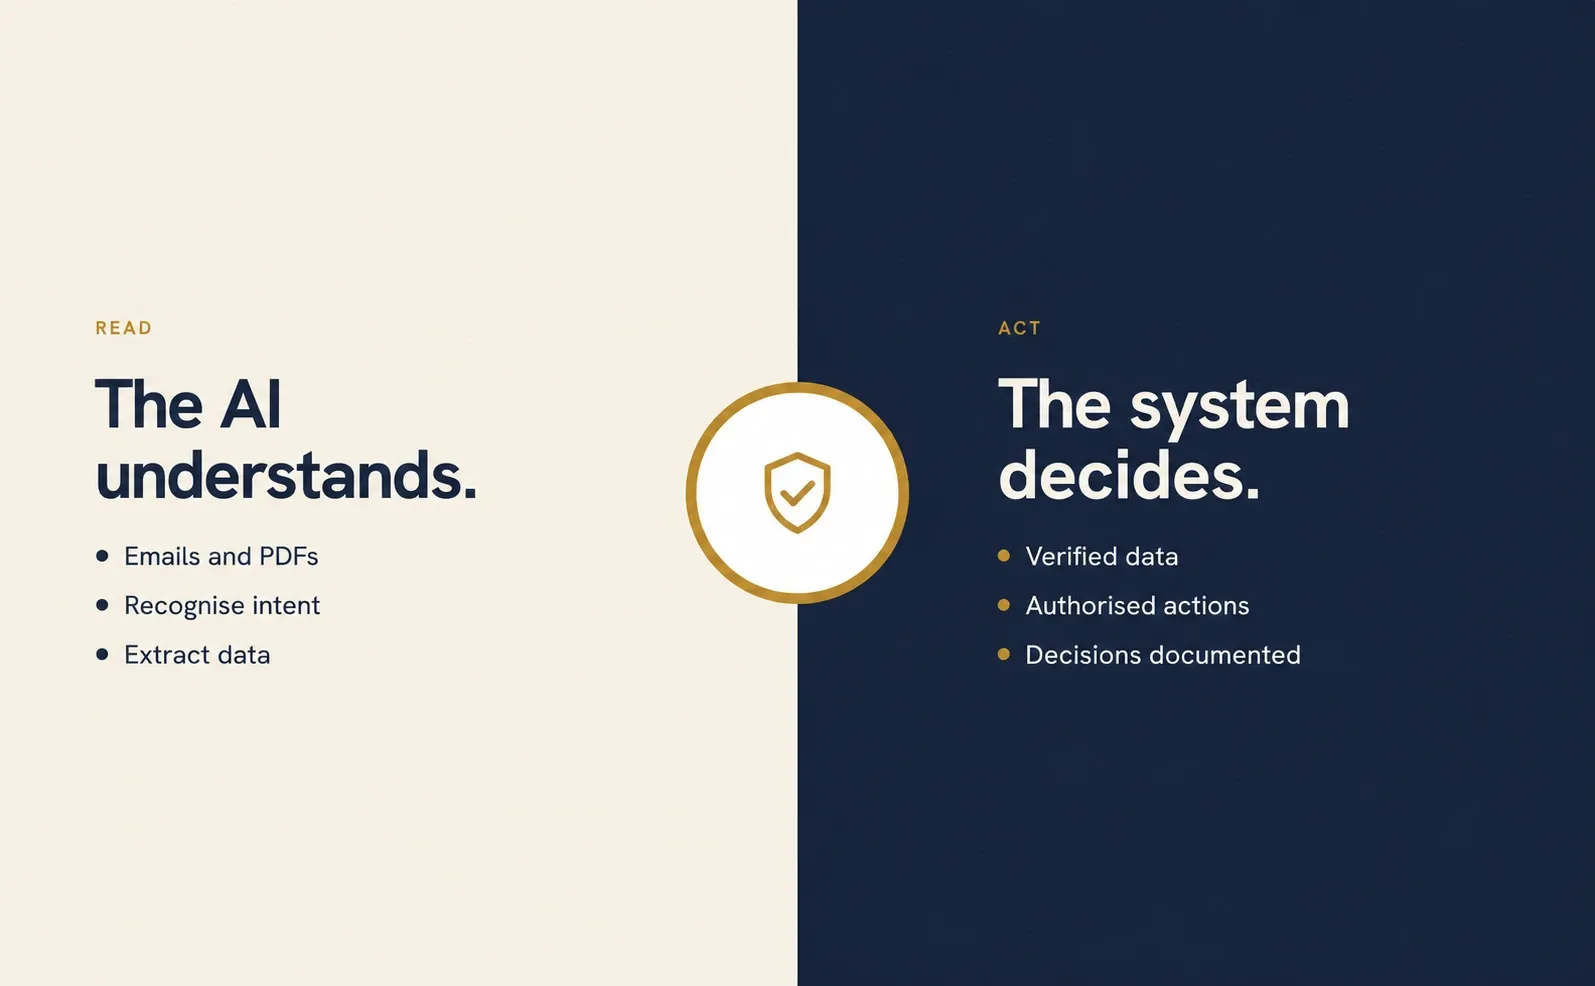 Security
Expert article 5 min
The AI understood the email. The payment still went to fraudsters.
AI agents can take work off a team’s hands. Whether they may act on a request is a separate business decision.
Read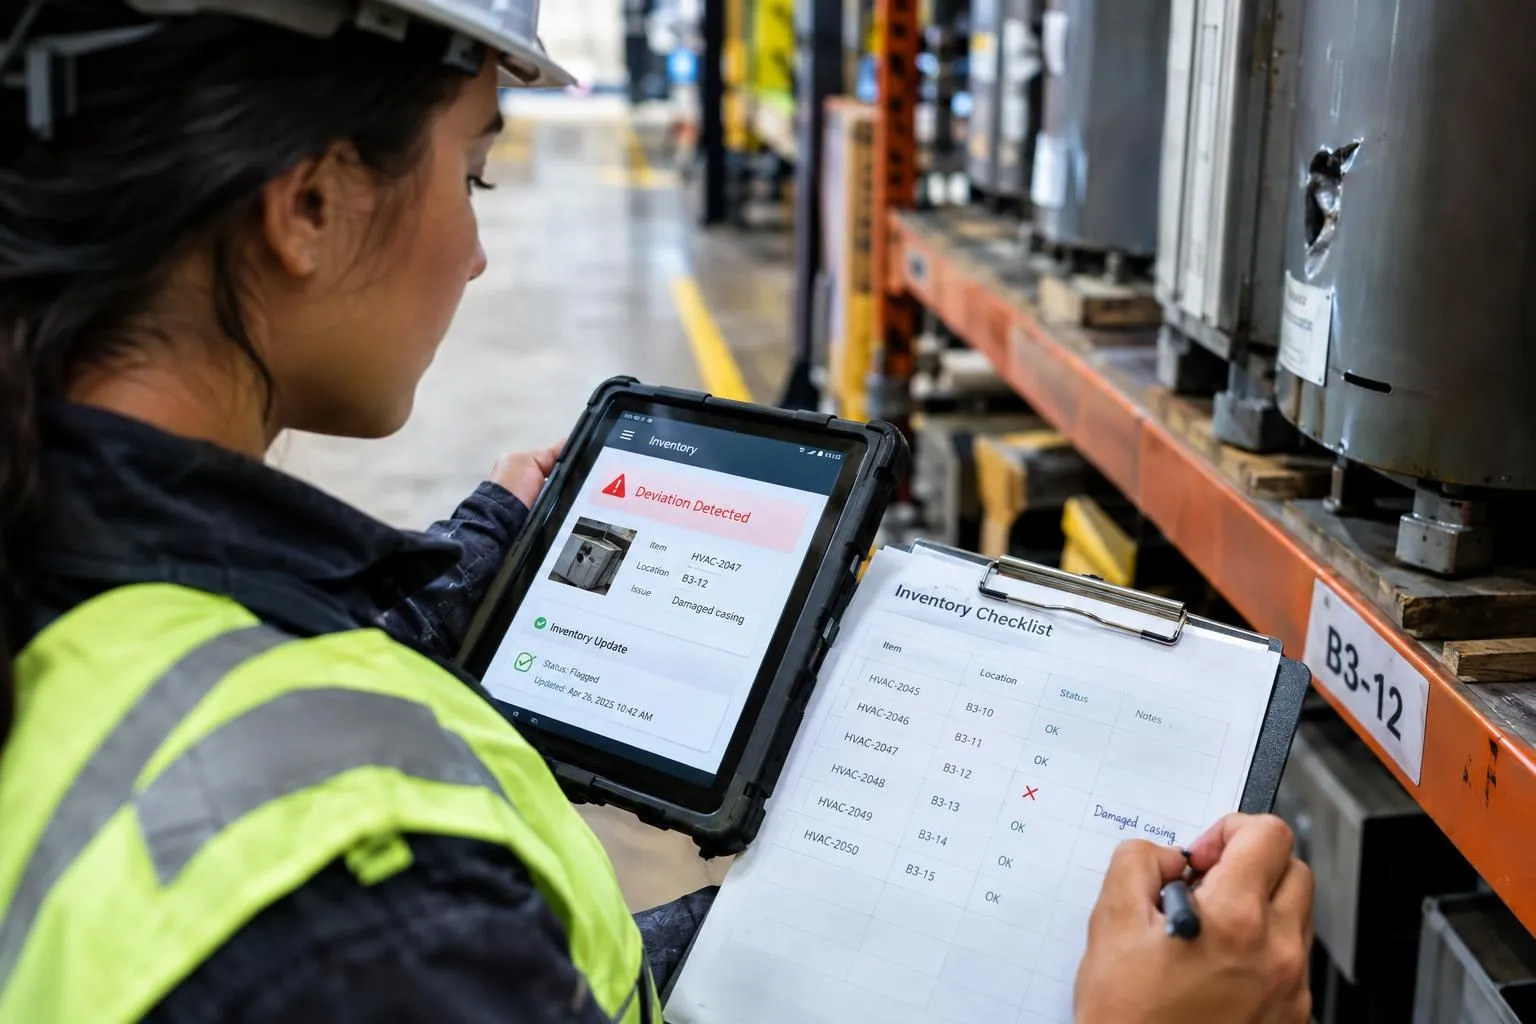 Security
4 min
Local Deviation Scanning and Inventory Updates: Closing the Loop on PIRN and BEAM Integration
Today marks a pivotal advance in operational clarity for deviation management: Helpifyr/JaddaHelpifyr now supports local deviation detection, consult, and inventory updates directly within the PIRN layer, tightly integrated with the BEAM contract and inventory model. This closes the feedback loop for field operators and system integrators, ensuring that deviations are recognized, validated, and reflected in the source-of-truth inventory with minimal latency and maximal traceability.
Read Security
3 min
No More Shortcuts: Enforcing Canonical Mail Preview and Readback Paths via Fabric Admission
Today's work closes a subtle but critical loophole in the Helpifyr / JaddaHelpifyr stack: all mail preview, M365 Exchange, and Weft readbacks now flow strictly through the Fabric admission layer. This architectural enforcement eliminates direct backend shortcuts, ensuring that every access is policy-governed, auditable, and consistent with the platform's security guarantees. The result is a single, reliable source of truth for mail data access and a foundation for future capability extensions.
Read