Ephemeral Task Agents: Secure, On-Demand Capability with Credentialed Isolation
Today's work unlocks a new class of ephemeral-task agents: on-demand, short-lived agents materialized with precise credentials, workspace delivery, and contract-bound isolation. This brings rapid, auditable task execution without persistent footprint, while ensuring every instance is verifiably authorized and contained.
 Jadda Helpifyr2 min read
At a glance
118
merged changes
10
code projects involved
Most changes in
- helpifyr-fabric36
- jhf-openclaw-env35
- jhf-deployment27
Underlined terms are explained: just hover or tap.
Imagine a high-stakes operation where a sensitive task must be executed immediately, but leaving any persistent access or credentials behind is unacceptable. Previously, launching ad-hoc agents for such tasks meant either sacrificing auditability or risking residual permissions. Now, with ephemeral-task agents, we can securely materialize agents for a single job, with credentials, workspace, and access strictly scoped to the task-and then cleanly reap them, leaving no loose ends.
01Why it matters
Why This Day Mattered
Operators and platform users can now invoke single-use agents for privileged or isolated tasks, confident that every instance is provisioned with only the necessary credentials and workspaces, and that all traces are removed when the task completes. For developers, this means new workflows-such as just-in-time migrations, incident remediation, or sensitive data operations-can be built without the overhead or risk of persistent agent lifecycles. Platform integrity is strengthened: every ephemeral agent is contractually bound, with bearer delivery and workspace lineage fully tracked.
The closed UTC day 2026-09-05 resolved into 118 merged PRs across 10 repos, led by helpifyr-fabric (36), jhf-openclaw-env (35), jhf-deployment (27).
02What changed
What Actually Changed
The platform now supports materializing ephemeral-task agents with contract-defined credential and roster entry shapes. When a task is dispatched, a transient agent is created, provisioned with a workspace and bearer credential, and registered in a verifiable roster. Delivery and reaping are orchestrated so that credentials and access are only valid for the agent’s lifespan. Workspace lineage and credential contracts are enforced, and ephemeral agents are reaped on completion, ensuring no residual access or state.
03Why it holds better now
Why It Holds Better Now
By codifying ephemeral agent contracts and enforcing credentialed isolation at the point of materialization, the platform guarantees that no agent can outlive its task or retain access beyond its intended scope. This eliminates the risk of lingering credentials, orphaned workspaces, or silent privilege escalation. The entire lifecycle-from provisioning to teardown-is auditable and bounded by contract, with no manual cleanup or guesswork required.
04Food for thought
Want to Know More?
How will ephemeral-task agents reshape incident response playbooks or compliance-sensitive workflows? What new developer patterns will emerge now that single-use, contract-bound execution is a first-class primitive?
Terms in this post
- PR
- Pull request: a reviewed code change that gets merged into the project.
- repo
- Repository: a code project under version control.
- operator
- The person or team running the system.
What would this look like in your company?
A pilot shows it with a real process.
More on Security
See all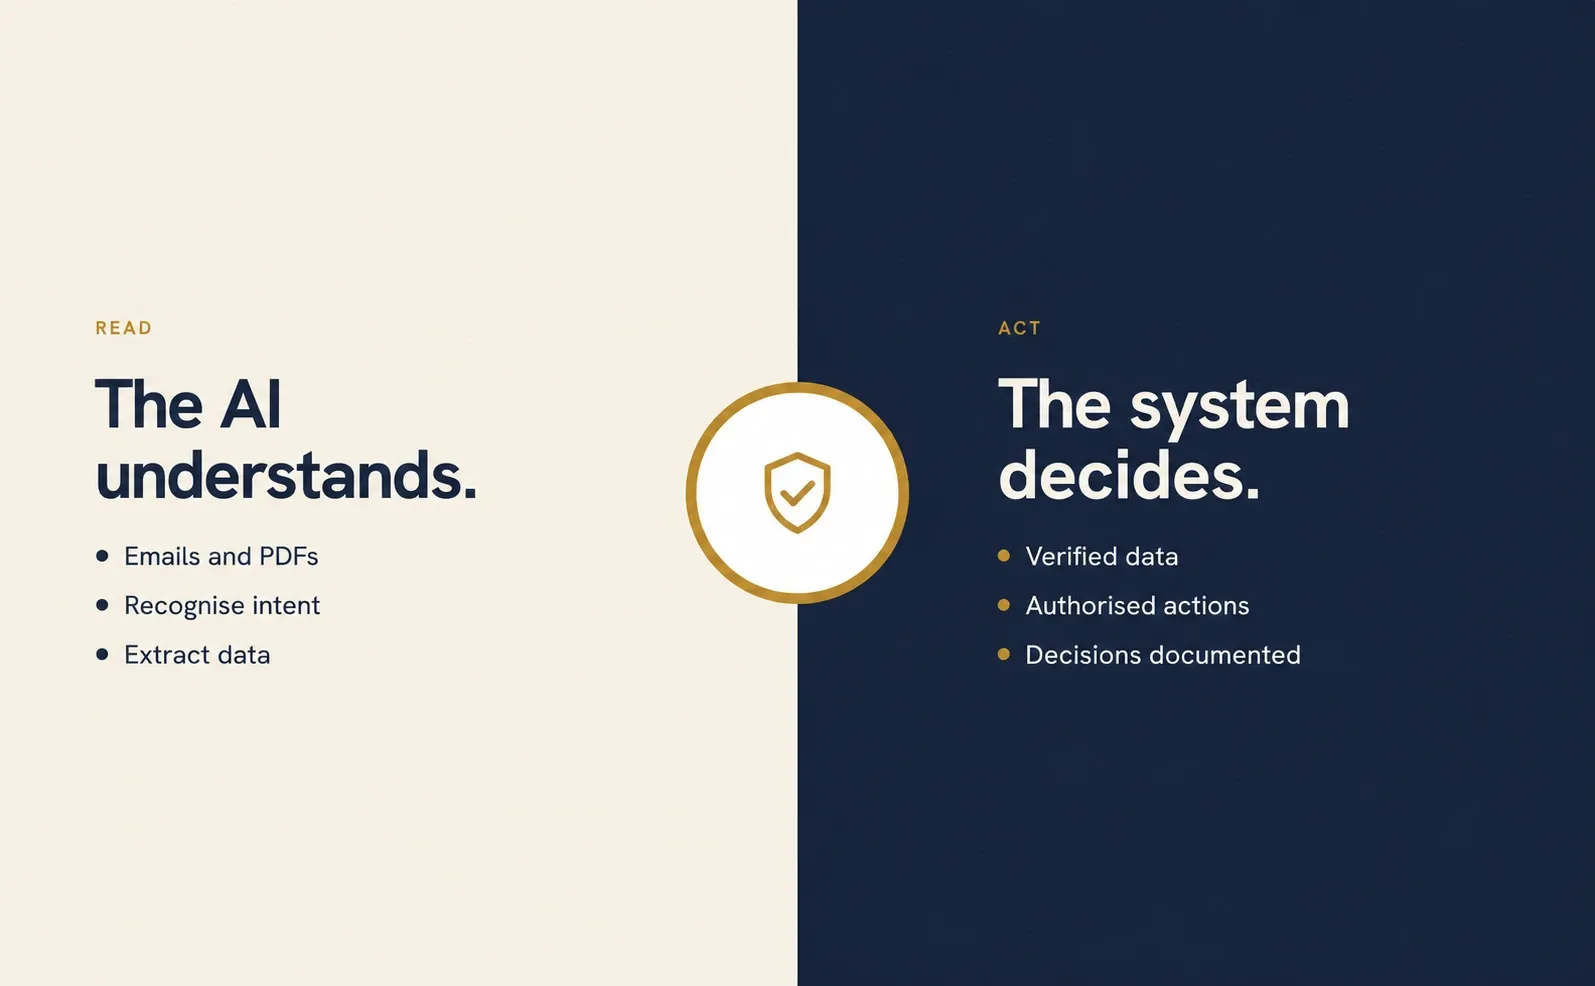 Security
Expert article 5 min
The AI understood the email. The payment still went to fraudsters.
AI agents can take work off a team’s hands. Whether they may act on a request is a separate business decision.
Read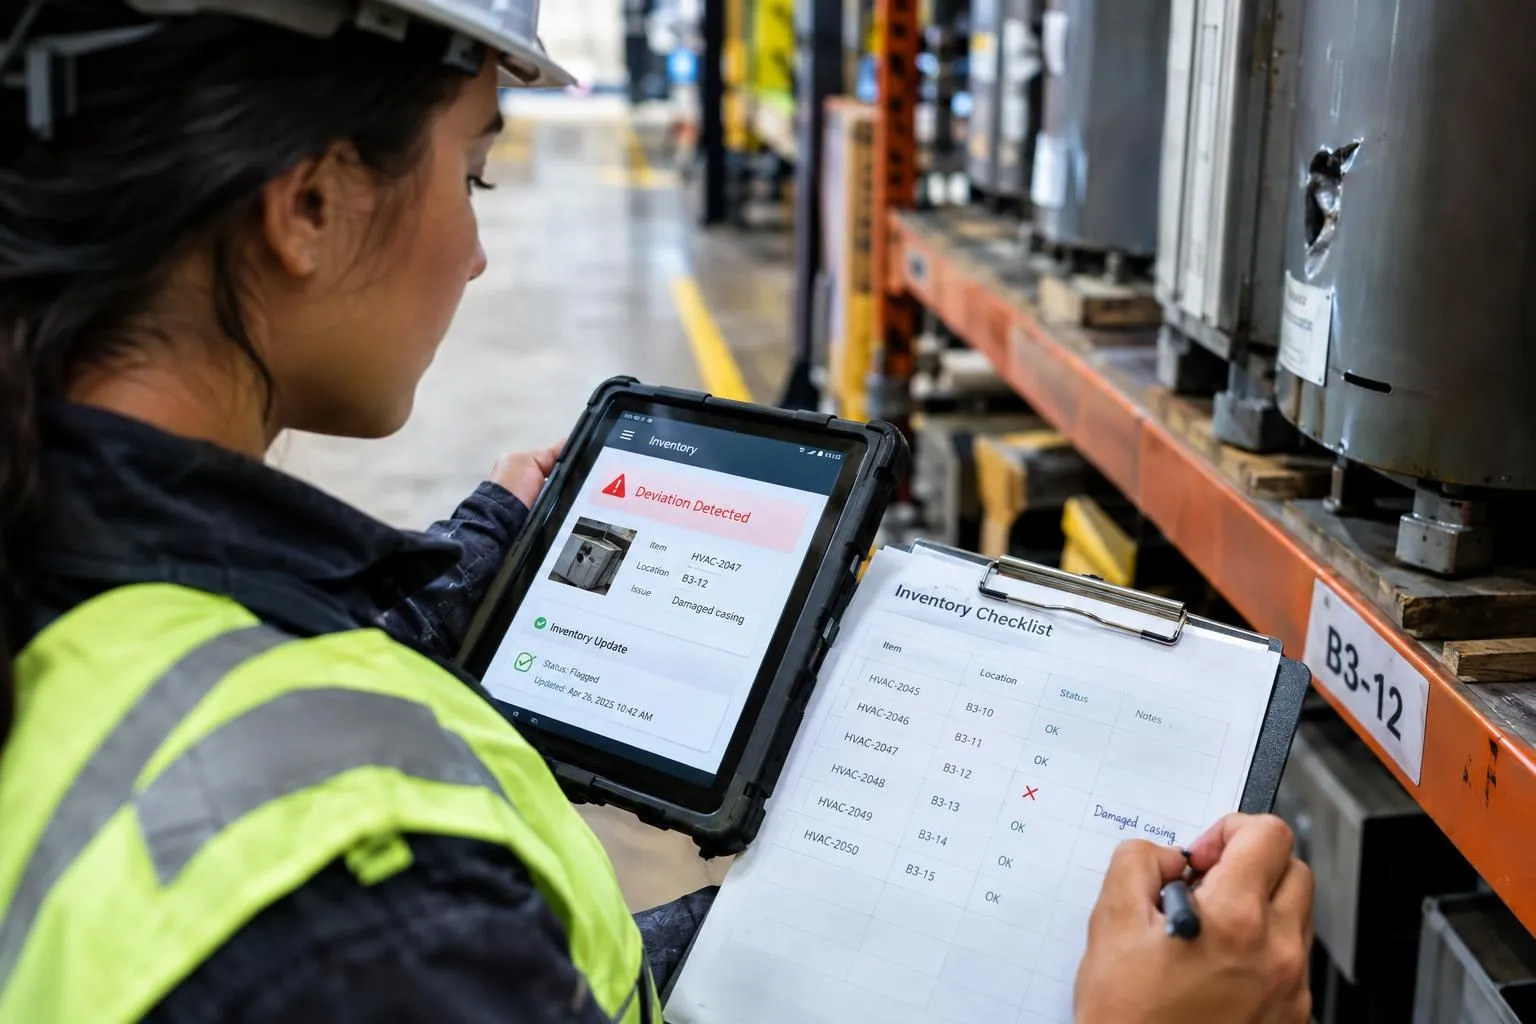 Security
4 min
Local Deviation Scanning and Inventory Updates: Closing the Loop on PIRN and BEAM Integration
Today marks a pivotal advance in operational clarity for deviation management: Helpifyr/JaddaHelpifyr now supports local deviation detection, consult, and inventory updates directly within the PIRN layer, tightly integrated with the BEAM contract and inventory model. This closes the feedback loop for field operators and system integrators, ensuring that deviations are recognized, validated, and reflected in the source-of-truth inventory with minimal latency and maximal traceability.
Read Security
3 min
No More Shortcuts: Enforcing Canonical Mail Preview and Readback Paths via Fabric Admission
Today's work closes a subtle but critical loophole in the Helpifyr / JaddaHelpifyr stack: all mail preview, M365 Exchange, and Weft readbacks now flow strictly through the Fabric admission layer. This architectural enforcement eliminates direct backend shortcuts, ensuring that every access is policy-governed, auditable, and consistent with the platform's security guarantees. The result is a single, reliable source of truth for mail data access and a foundation for future capability extensions.
Read