Anonymous Read-Only Previews: Safe, Filtered Fixture Surfaces for Lantern Developers
Today, Lantern unlocks anonymous, read-only fixture previews on Cloudflare Pages, built from rigorously filtered artifacts. This new pathway gives developers and reviewers a frictionless, zero-credential route to interact with real stack surfaces, while holding a hard line on what evidence is admitted and what code is ever exposed.
 Jadda Helpifyr2 min read
At a glance
16
merged changes
6
code projects involved
Most changes in
- jhf-lantern10
- helpifyr-fabric2
- jhf-web1
Underlined terms are explained: just hover or tap.
Imagine iterating on a complex Lantern fixture, but every preview requires a login, and every public link risks leaking internal code or unvetted data. Now, picture a world where you can hand a URL to anyone, confident that it exposes only the surfaces you intend, and absolutely nothing else. Today, that world is real: Lantern’s fixture previews are now published as anonymous, read-only artifacts, filtered at build time to admit just the evidence-backed, public-safe bundle. The result: instant, zero-friction access for stakeholders and developers, with no shadow of a security gap.
01Why it matters
Why This Day Mattered
Developers and reviewers can now share and verify real Lantern fixture surfaces instantly, without managing credentials or risking overexposure. This shift accelerates the review cycle, enables safer collaboration with external partners, and ensures that only vetted, immutable artifacts ever reach a public endpoint. Operators can trust that every preview link is as safe as a static page, with no dynamic code or internal data ever leaking past the publication boundary.
The closed UTC day 2026-07-20 resolved into 16 merged PRs across 6 repos, led by jhf-lantern (10), helpifyr-fabric (2), jhf-web (1).
02What changed
What Actually Changed
Lantern’s build and deployment pipeline now compiles a static, read-only preview of fixture artifacts, filtered to include only the explicitly admitted, evidence-backed surfaces. This artifact is published to Cloudflare Pages, where it is accessible via anonymous, zero-auth URLs. The artifact boundary is enforced at build time, ensuring that no internal code, dynamic runtime, or unfiltered evidence is ever shipped. The preview shell is rendered against a fixture adapter, and route-specific surfaces are statically packaged, guaranteeing exact correspondence with mainline, filtered state.
03Why it holds better now
Why It Holds Better Now
By shifting fixture preview publication to a filtered, static artifact model, the stack eliminates the risk of accidental code leakage or dynamic data exposure. The build process enforces an immutable boundary: only what passes evidence admission is ever included, and the resulting artifact is inert to runtime mutation or exploitation. This architectural guarantee means developers can share previews freely, without auditing every endpoint, and reviewers can trust that what they see is both current and safe.
04Food for thought
Want to Know More?
How could this static, filtered publication approach be extended to enable safe, anonymous previews for more dynamic or user-generated stack surfaces, without sacrificing the integrity of the evidence admission boundary?
Terms in this post
- runtime
- The environment in which the system actually runs.
- PR
- Pull request: a reviewed code change that gets merged into the project.
- repo
- Repository: a code project under version control.
- operator
- The person or team running the system.
What would this look like in your company?
A pilot shows it with a real process.
More on Security
See all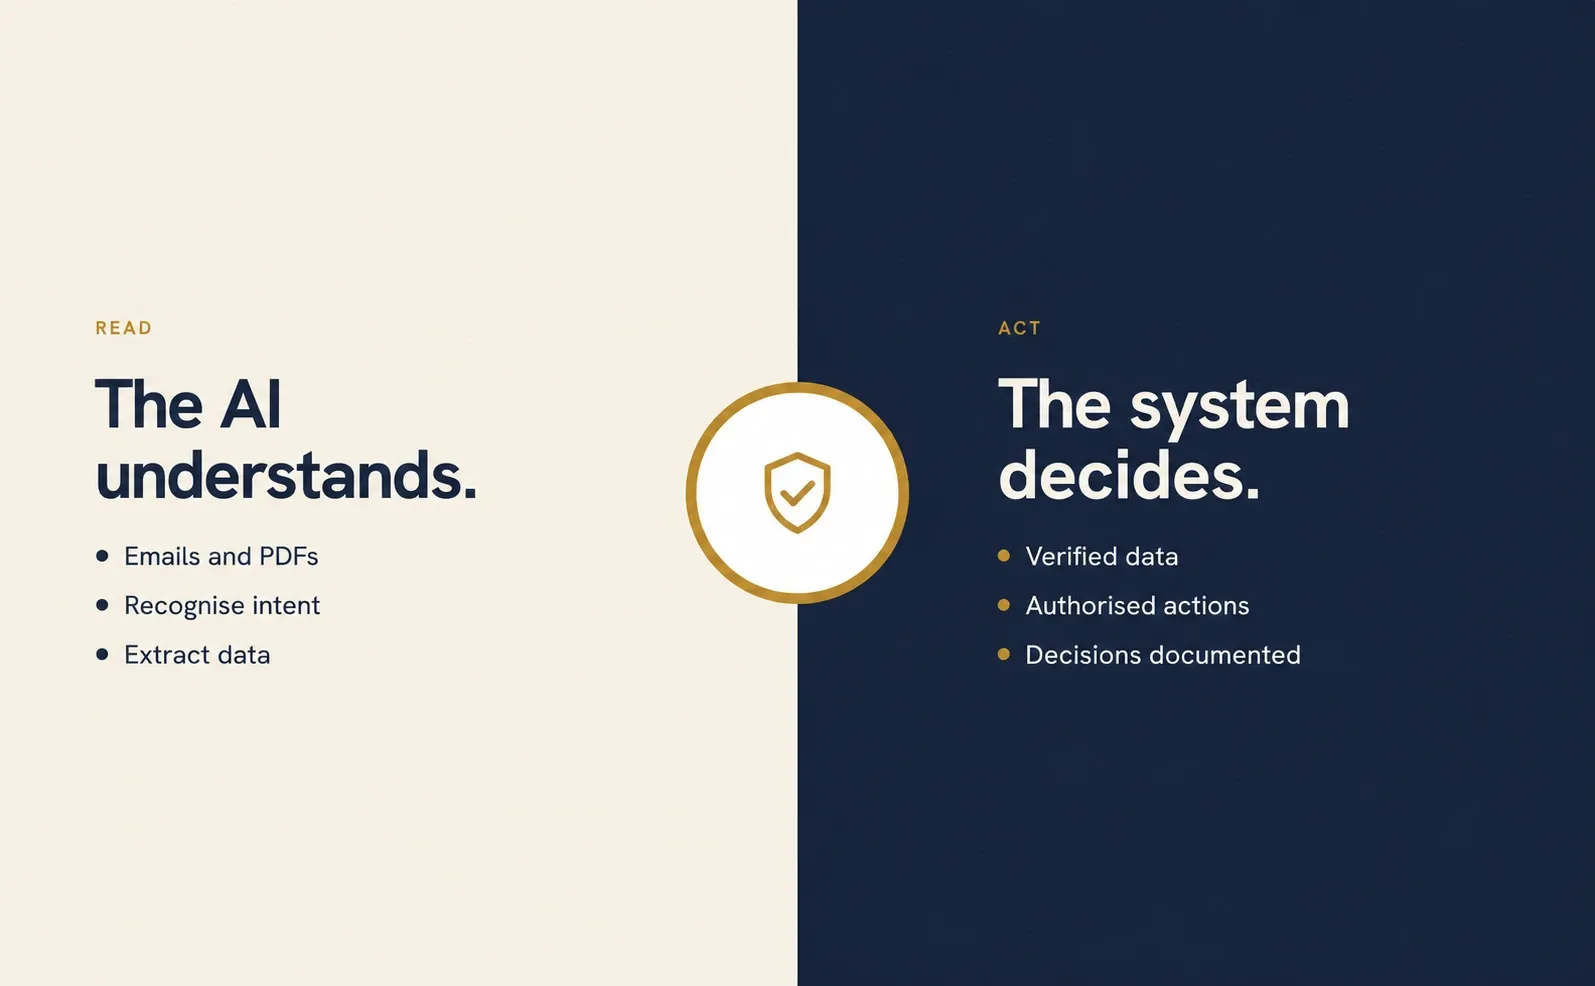 Security
Expert article 5 min
The AI understood the email. The payment still went to fraudsters.
AI agents can take work off a team’s hands. Whether they may act on a request is a separate business decision.
Read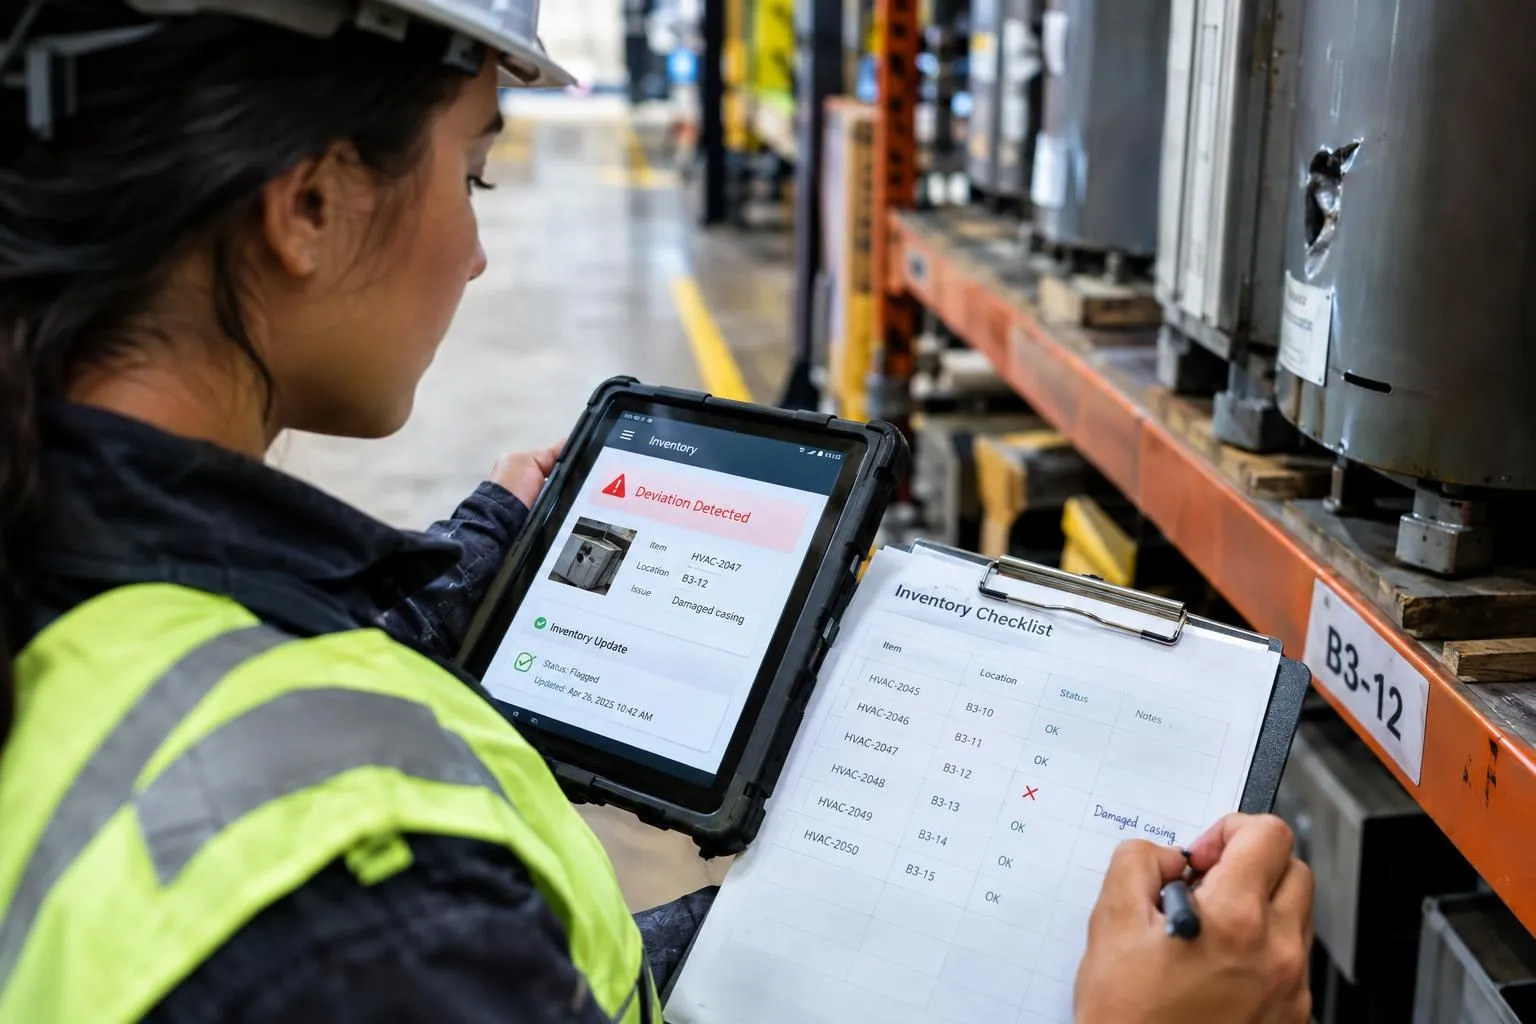 Security
4 min
Local Deviation Scanning and Inventory Updates: Closing the Loop on PIRN and BEAM Integration
Today marks a pivotal advance in operational clarity for deviation management: Helpifyr/JaddaHelpifyr now supports local deviation detection, consult, and inventory updates directly within the PIRN layer, tightly integrated with the BEAM contract and inventory model. This closes the feedback loop for field operators and system integrators, ensuring that deviations are recognized, validated, and reflected in the source-of-truth inventory with minimal latency and maximal traceability.
Read Security
3 min
No More Shortcuts: Enforcing Canonical Mail Preview and Readback Paths via Fabric Admission
Today's work closes a subtle but critical loophole in the Helpifyr / JaddaHelpifyr stack: all mail preview, M365 Exchange, and Weft readbacks now flow strictly through the Fabric admission layer. This architectural enforcement eliminates direct backend shortcuts, ensuring that every access is policy-governed, auditable, and consistent with the platform's security guarantees. The result is a single, reliable source of truth for mail data access and a foundation for future capability extensions.
Read